
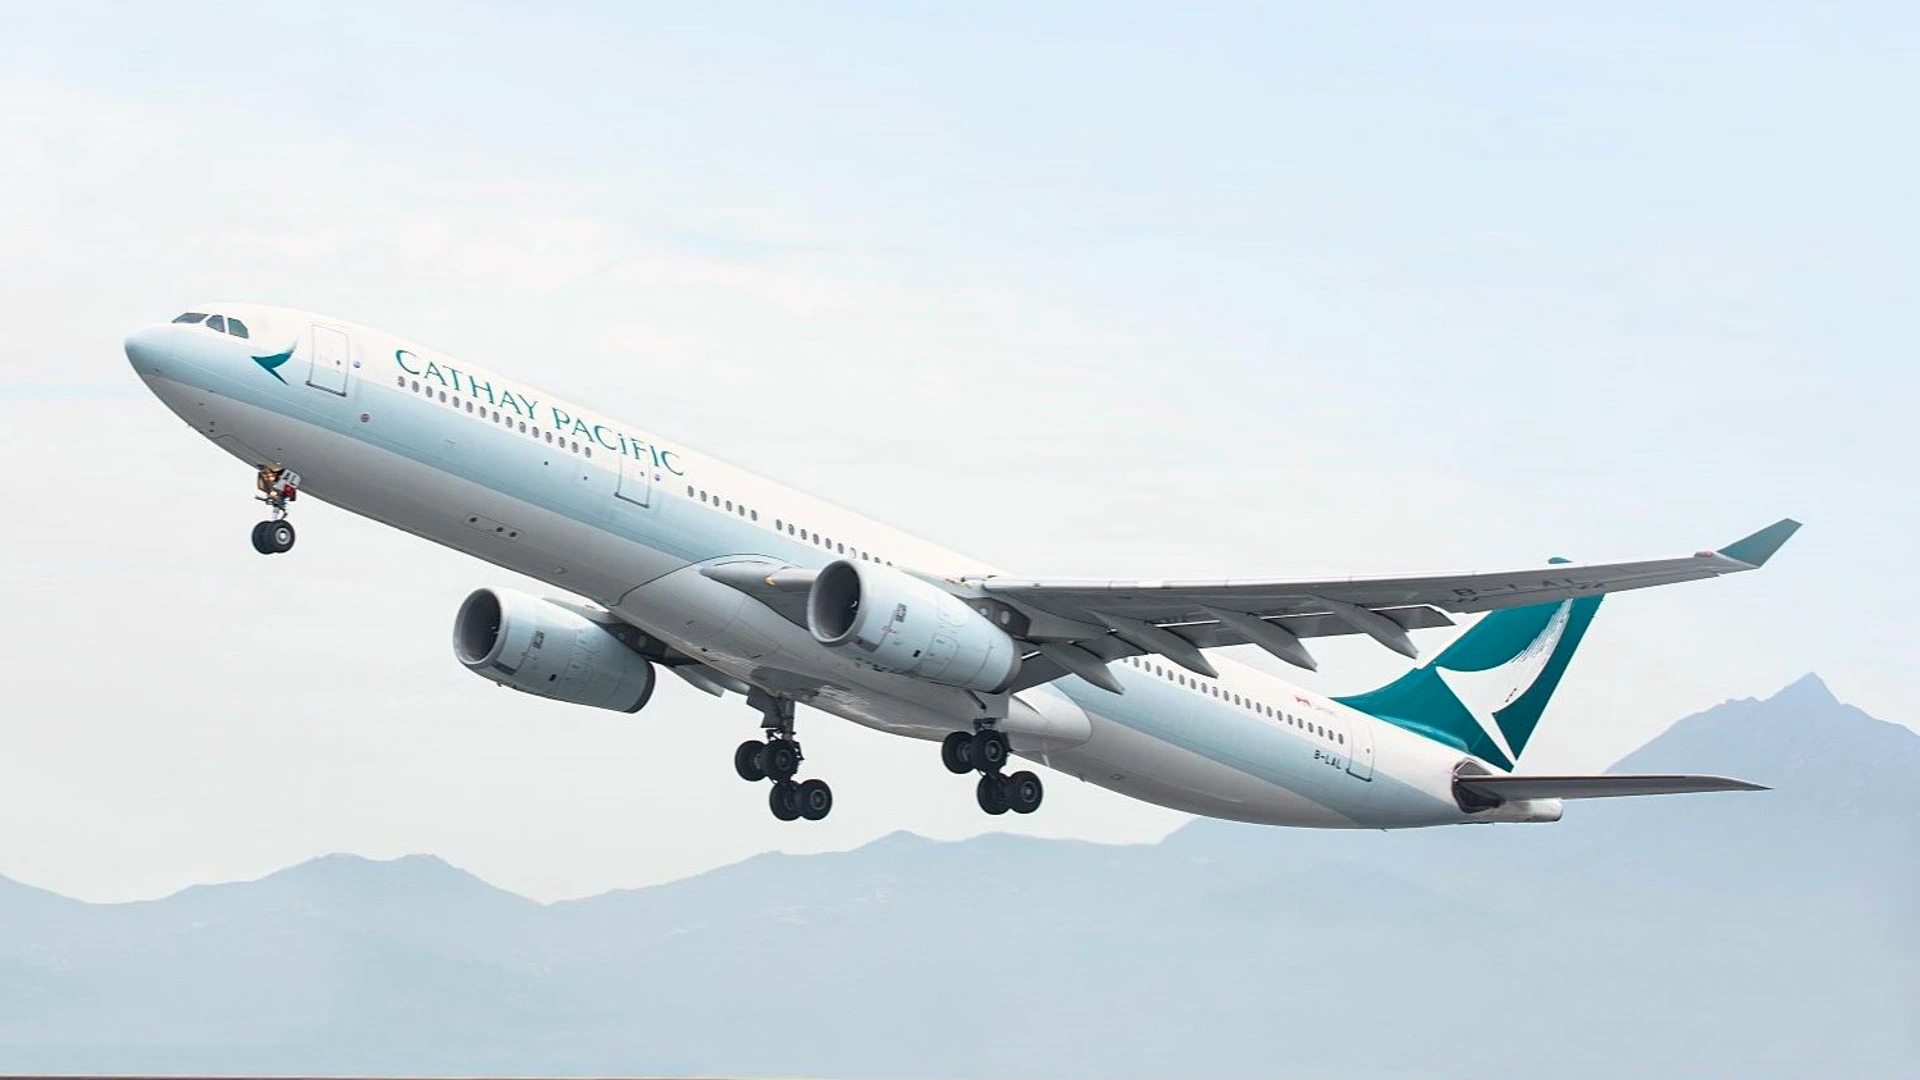
HONG KONG– Cathay Pacific Airways (CX) has disclosed that unauthorized access to its third-party technology provider’s systems exposed information linked to approximately 53,000 flight bookings. The incident involved Amadeus IT Group, a global travel technology company whose services are used by hundreds of airlines, and affected reservation records created between August 2023 and September 2026.
The airline said the breach did not involve its own systems and has not disrupted its operations. Although booking references, passenger names and flight details were accessed in most cases, Cathay Pacific has found no evidence that payment or financial information was compromised.

Amadeus Data Breach Affects Cathay
Cathay Pacific said Amadeus notified it about the security incident on October 28, 2026, and provided further details the following day. According to the information supplied by the technology provider, an unauthorised party used login credentials assigned to a system account to access travel reservation data.
The affected records included approximately 53,000 bookings associated with Cathay Pacific. In most cases, the accessed information included passenger names, booking reference numbers and flight details, which can reveal details of a traveller’s itinerary.
A smaller number of records may also have contained additional personal information. This included email addresses, telephone contacts, travel document details and frequent flyer numbers, although Cathay did not disclose how many bookings fell into this category.
The airline stressed that there was no evidence that financial or payment details had been accessed. Amadeus also told Cathay that it had not identified evidence of the affected information being misused.
Airline Security Measures
Amadeus confirmed that it had taken steps to contain the incident, including resetting the affected password and strengthening monitoring and detection across its systems.
The company has not identified evidence that the accessed information has been misused so far.
Cathay Pacific said the incident did not affect its internal systems or flight operations. The Hong Kong-based carrier has informed the relevant authorities and is continuing to examine the information supplied by Amadeus to establish which customers were affected.
The airline said it would contact affected customers individually once it had confirmed the relevant details. It also apologised for the concern and inconvenience caused by the incident, while reiterating that it takes the protection of customer information seriously.
Other Airlines Affected by the Breach
The incident has also prompted disclosures from other airlines that use Amadeus technology.
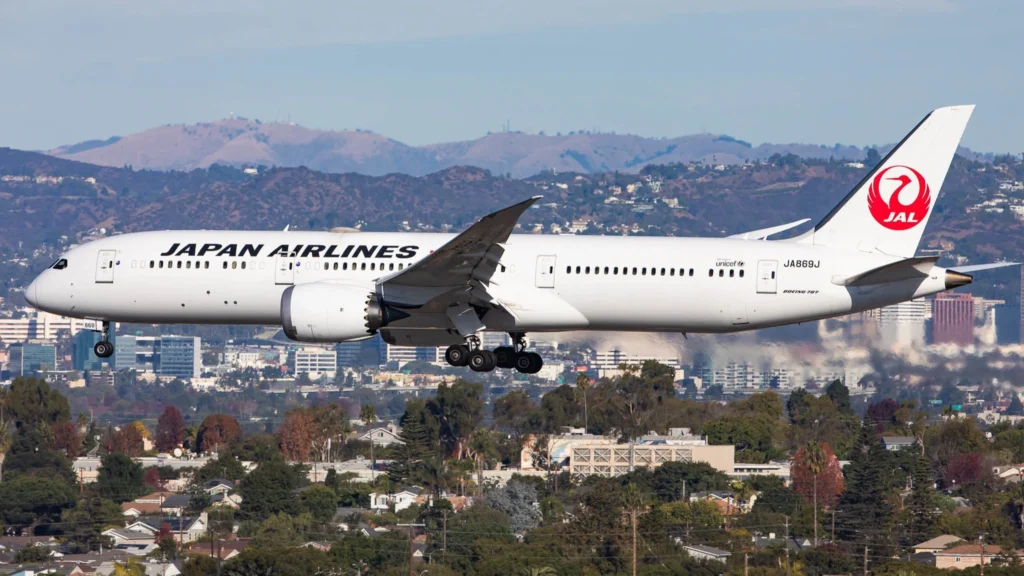
Japan Airlines (JL) and Japan Transocean Air reported that reservation information linked to approximately 92,000 customers may have been accessed, including names, booking references, travel dates, flight sectors and cabin classes.
All Nippon Airways (NH) separately reported that information relating to around 37,800 customers may have been accessed.
The airline said most affected records contained names and reservation details, while a smaller group also had contact information, passport details and frequent flyer numbers potentially exposed.
Korean Air (KE) and Asiana Airlines (OZ) have also reported unauthorised access involving Amadeus systems, SCMP flagged.
The disclosures indicate that the incident has affected multiple airline customers of the technology provider, although the figures released by individual carriers represent separate airline-specific impacts and should not be treated as a confirmed combined total.
Stay tuned with us. Further, follow us on social media for the latest updates.
Join us on Telegram Group for the Latest Aviation Updates. Subsequently, follow us on Google News
